Events - Hyvä
Meet Magento Germany 2026: The Day After the Win
October 23, 2026 - by Alexandru-Manuel Carabus
The evening before, LIQUIDLAB and Vitacom won Best Performance Improvement at HIVE Germany 2026. On 22 October we went back into the same building for Meet Magento Germany, trophy in the bag. A talk on why a clean security scan proves less than you think, Hyvä on accessibility testing with AI, and three things we're taking home.
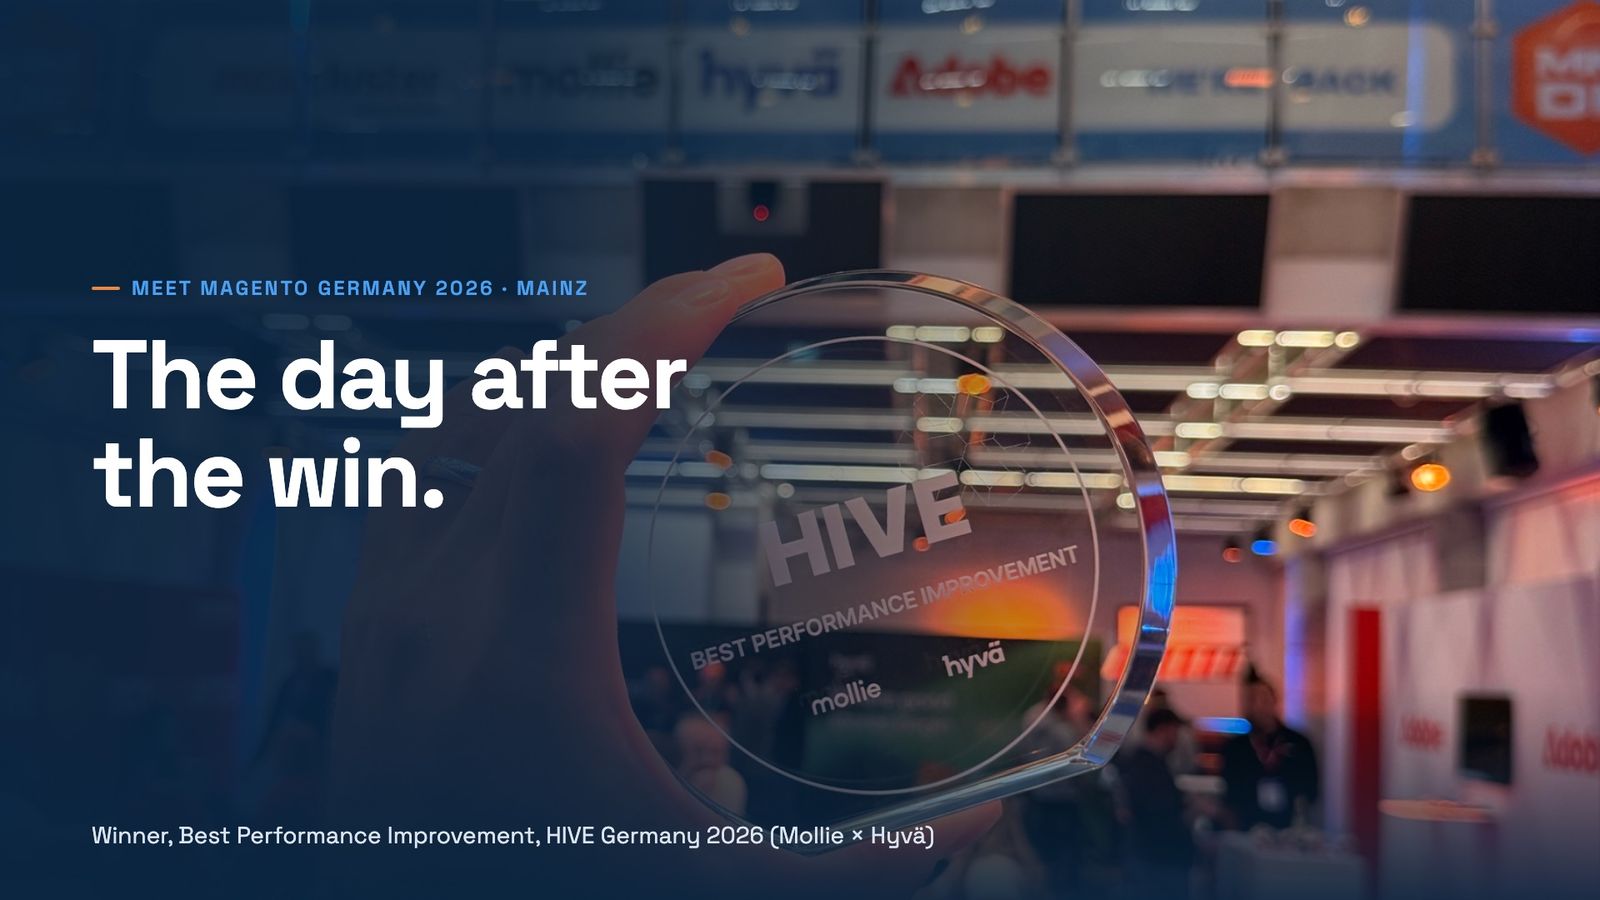
On the evening of 21 October, LIQUIDLAB and Vitacom won Best Performance Improvement at HIVE Germany 2026, voted by the room at the Pyramide Mainz. The next morning the same building opened again for Meet Magento Germany 2026, and we went back in, trophy in the bag.
The trophy came too
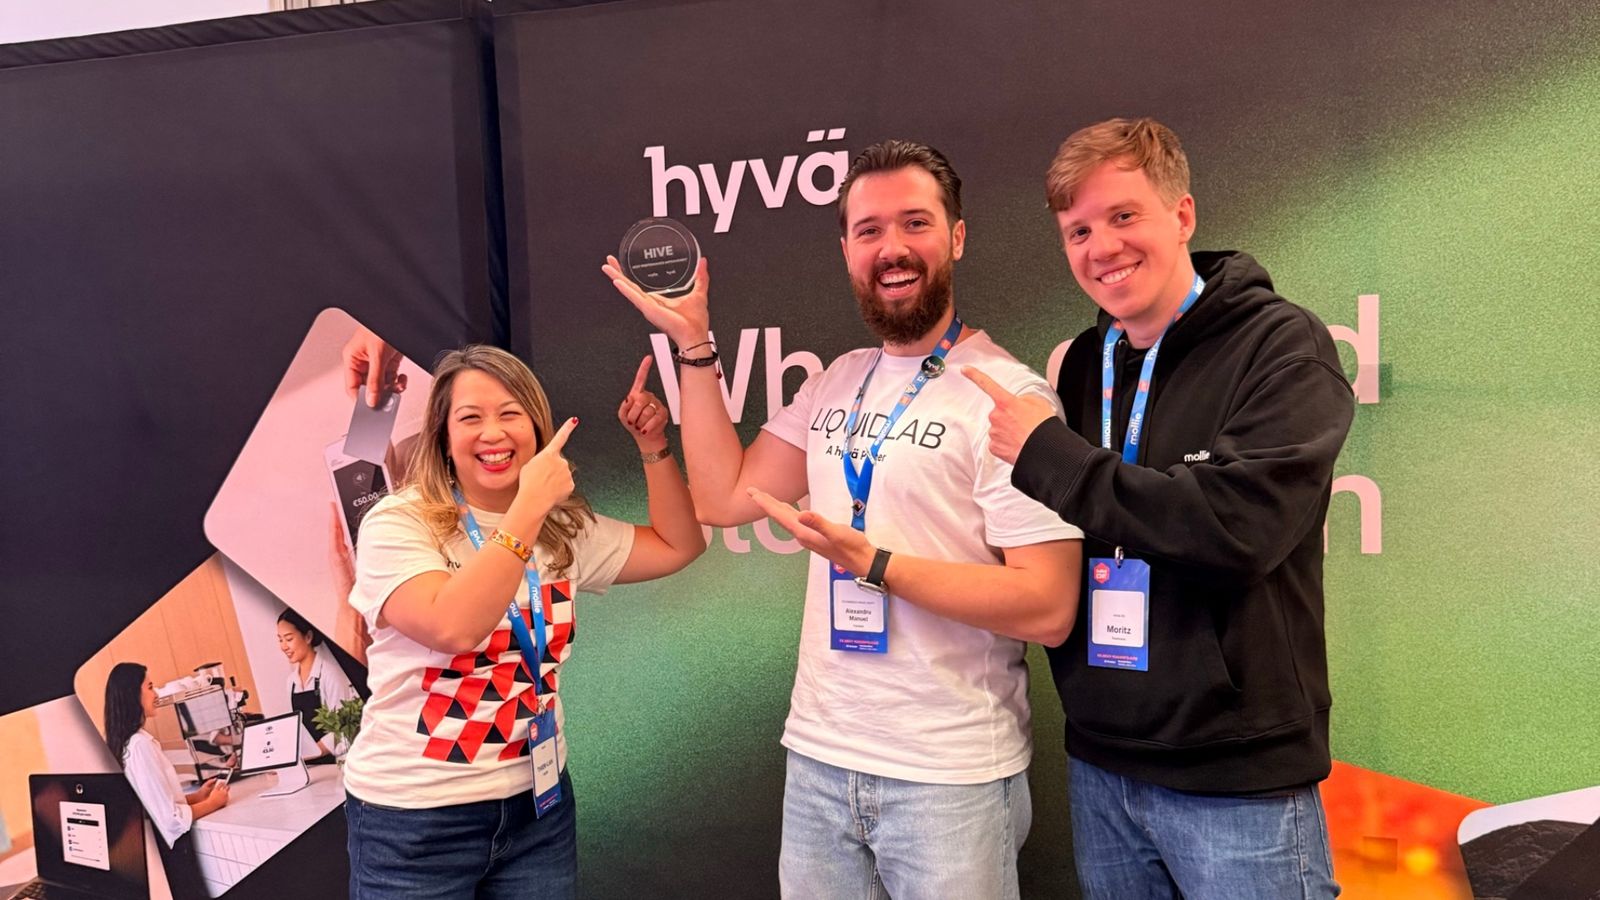
Before the afternoon talks, the trophy got its photo in the expo hall, under the sponsor banners. In the afternoon we stopped at the stand Hyvä and Mollie shared, the two companies behind HIVE, for a photo with their teams.
A clean security scan proves less than you think
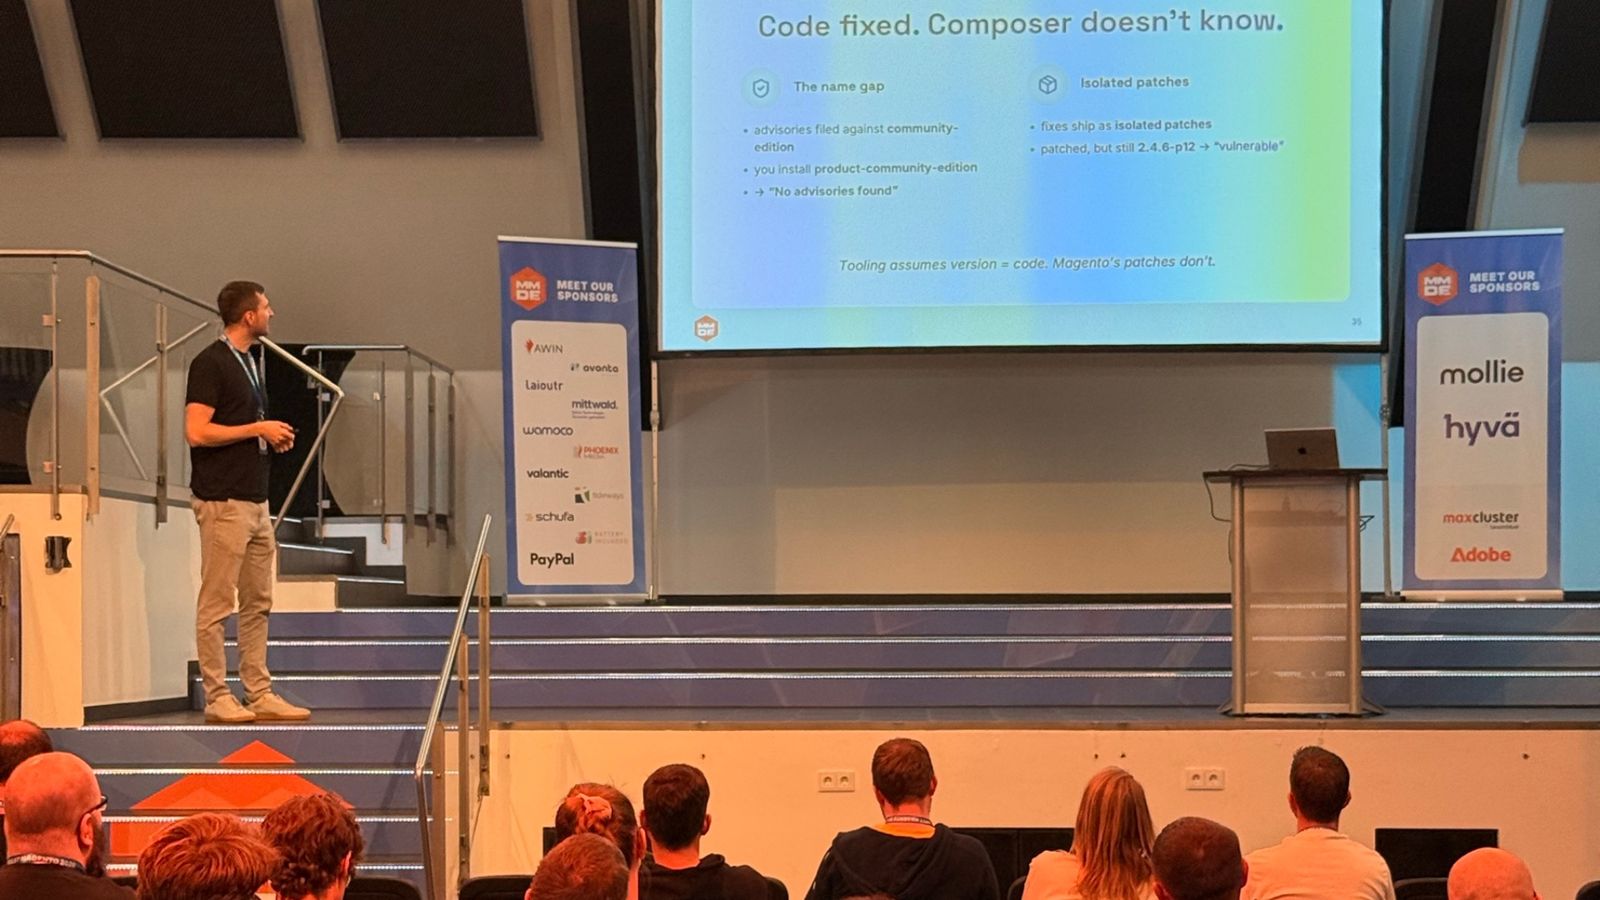
The talk we'd send every Magento merchant to came early in the afternoon, on the main stage. Its point fit on one slide: “Code fixed. Composer doesn't know.”
Most teams check their packages with composer audit, which compares the installed packages with public security feeds (GitHub and FriendsOfPHP). It matches by package name only. The speaker showed two ways that goes wrong on Magento:
- The name gap. Advisories are filed under magento/community-edition, but stores install magento/product-community-edition, so the audit reports “No advisories found”.
- Isolated patches. When Adobe ships a fix as an isolated patch, the code is fixed but the version number doesn't move. A store on 2.4.6-p12 with the patch applied still shows as “vulnerable”.
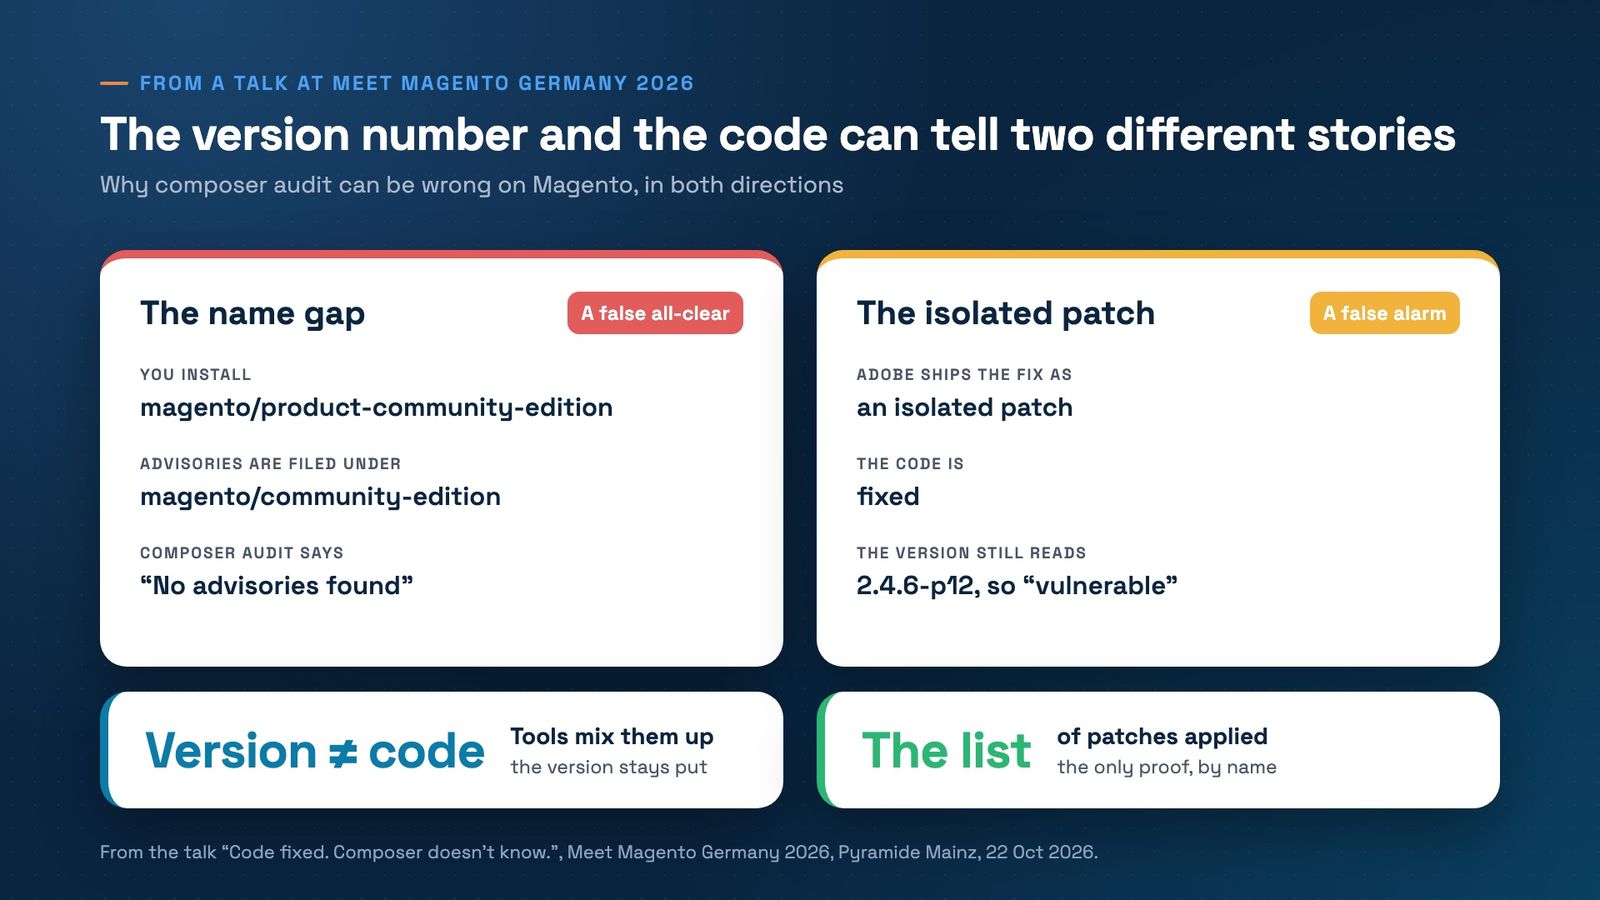
The slide's own summary: tooling assumes the version is the code, and Magento's patches don't work that way. The defence it gave: run composer audit --locked in CI, and remember that any repository can publish security advisories, private ones included, and the audit asks every one of them.
For a merchant, the lesson is simple. A green scan doesn't prove you're patched, and a red one doesn't prove you aren't. Ask your team for the list of patches actually applied, by name. We wrote about the two Magento patches in September. When we audited Vitacom in November 2025, 12 were missing.
Hyvä: accessibility testing with AI
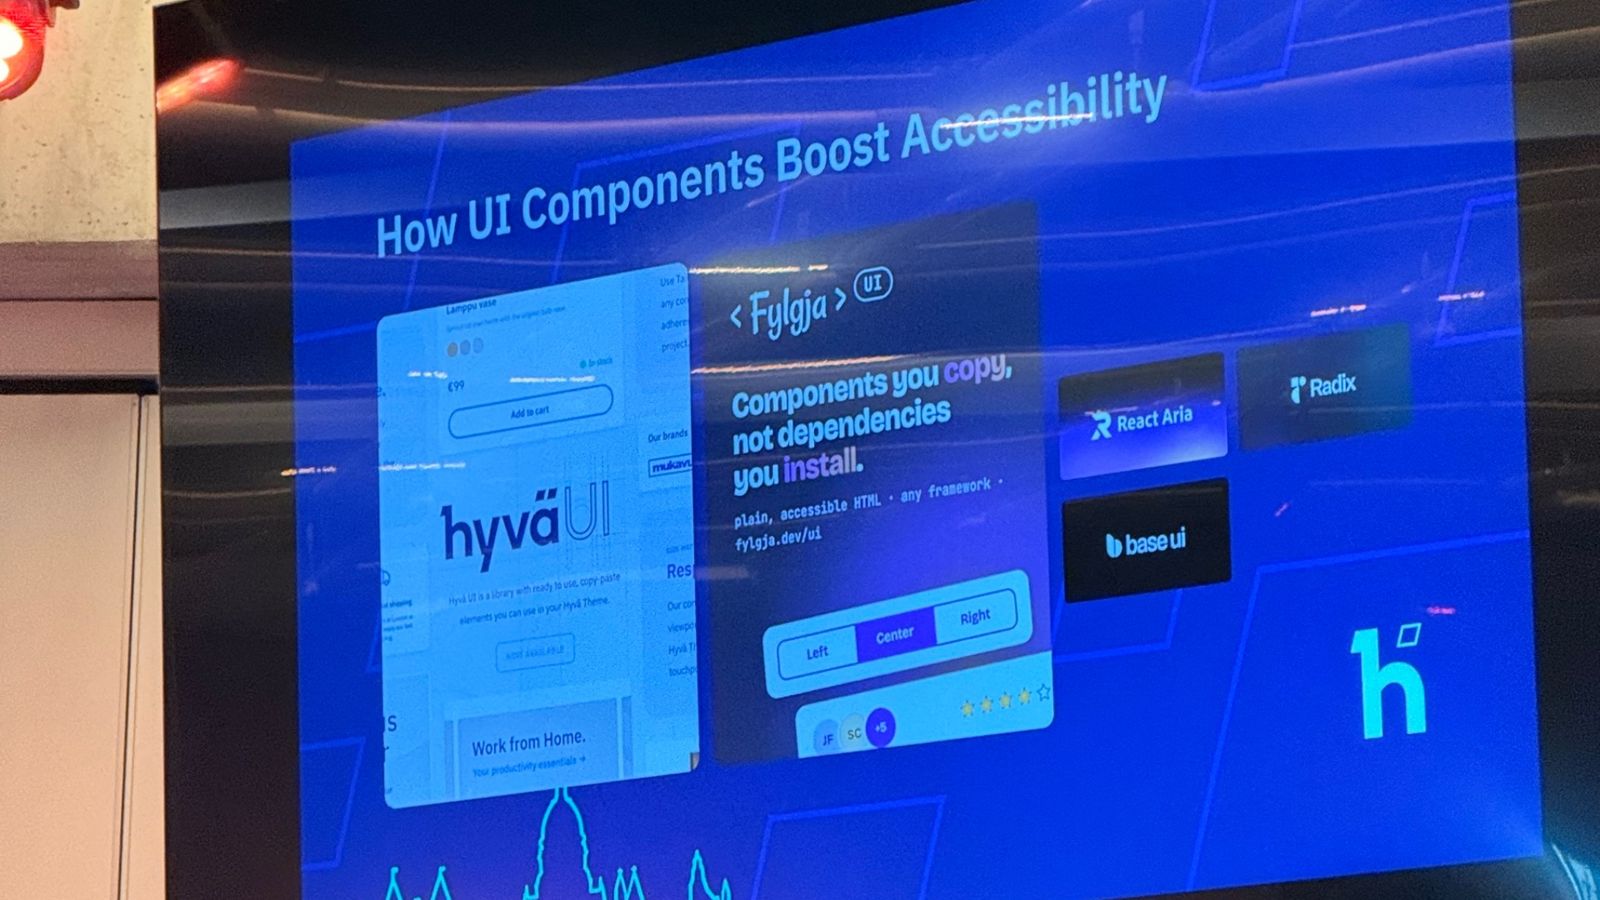
Later in the afternoon, Sean van Zuidam of Hyvä gave a talk called “Accessibility Testing with AI: Train your AI to become an A11Y expert”. It started from the components. Hyvä UI gives Hyvä stores ready-made elements you copy into your theme. The talk put it next to Fylgja UI (“components you copy, not dependencies you install”), React Aria, Radix and Base UI: libraries where accessible markup comes by default.
Then it showed an AI agent skill that runs a WCAG 2.2 Level AA audit on a page through the Chrome DevTools MCP. It checks heading hierarchy, landmark regions, colour contrast, ARIA attributes, keyboard navigation and target size.
Why it matters for a store: since 28 June 2025, the European Accessibility Act covers online shops selling in the EU, with an exemption for microenterprises. An accessibility check that runs on every release, like a speed check, is far easier than a big fix later.
Magento is… magic
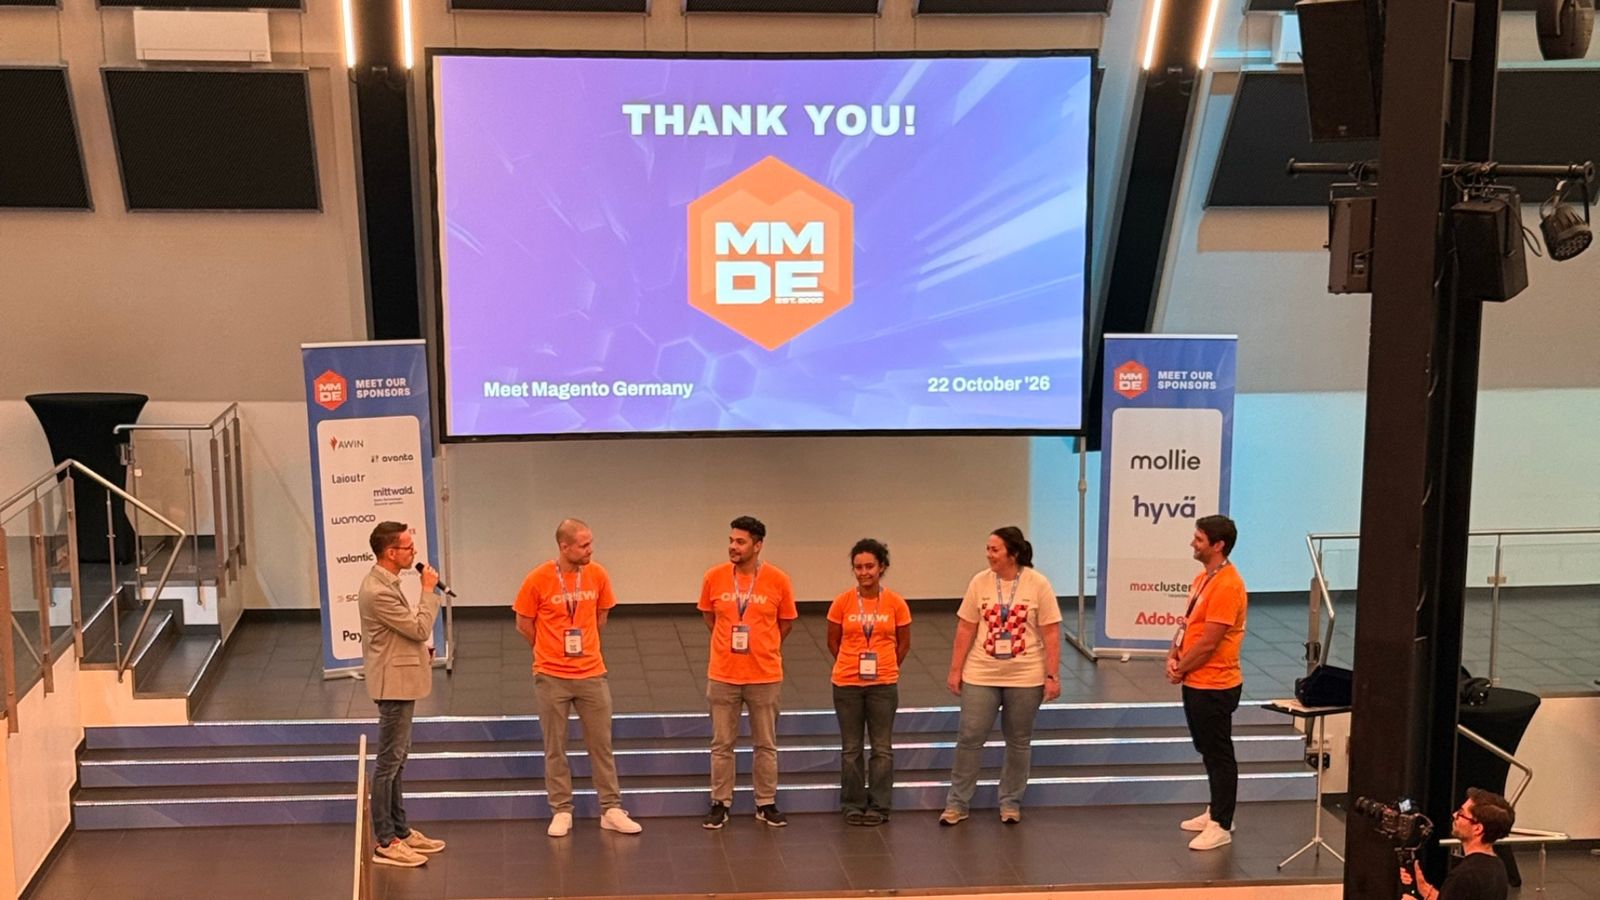
The day closed in the main hall. The organisers and their crew, in orange T-shirts, came on stage for the thank-you, then a closing talk ran under one line on the screen: “Magento is… MAGIC”. After a year of “is Magento dying?” questions, it was a good way to end a full hall.
What we're taking home
- Ask for patch names, not scan colours. A clean composer audit can miss Magento advisories, and an applied patch can still look vulnerable. The list of patches applied is the only proof.
- Accessibility belongs next to speed in your checks. Start from components that are accessible by default, then let an automated audit run on every release.
- The order still holds: security first, then the rest. The security talk pointed the same way we rebuilt Vitacom: three go-lives, security first. Speed, accessibility and polish come once the store is safe.
The evening ended over pinball and table football. Thank you to the Meet Magento Germany organisers and crew, and to Hyvä and Mollie, for two days in Mainz we won't forget.
On Magento and Hyvä
In the Liquid Framework, security patches are part of the service, next to nightly database backups, error tracking and health checks.
Want to know which patches your store really has? Book a free strategy call. We'll go through what's missing with you, and what to fix first.
Get the next article in your inbox
One email a month with new articles, speed fixes and the Magento security patches worth applying.